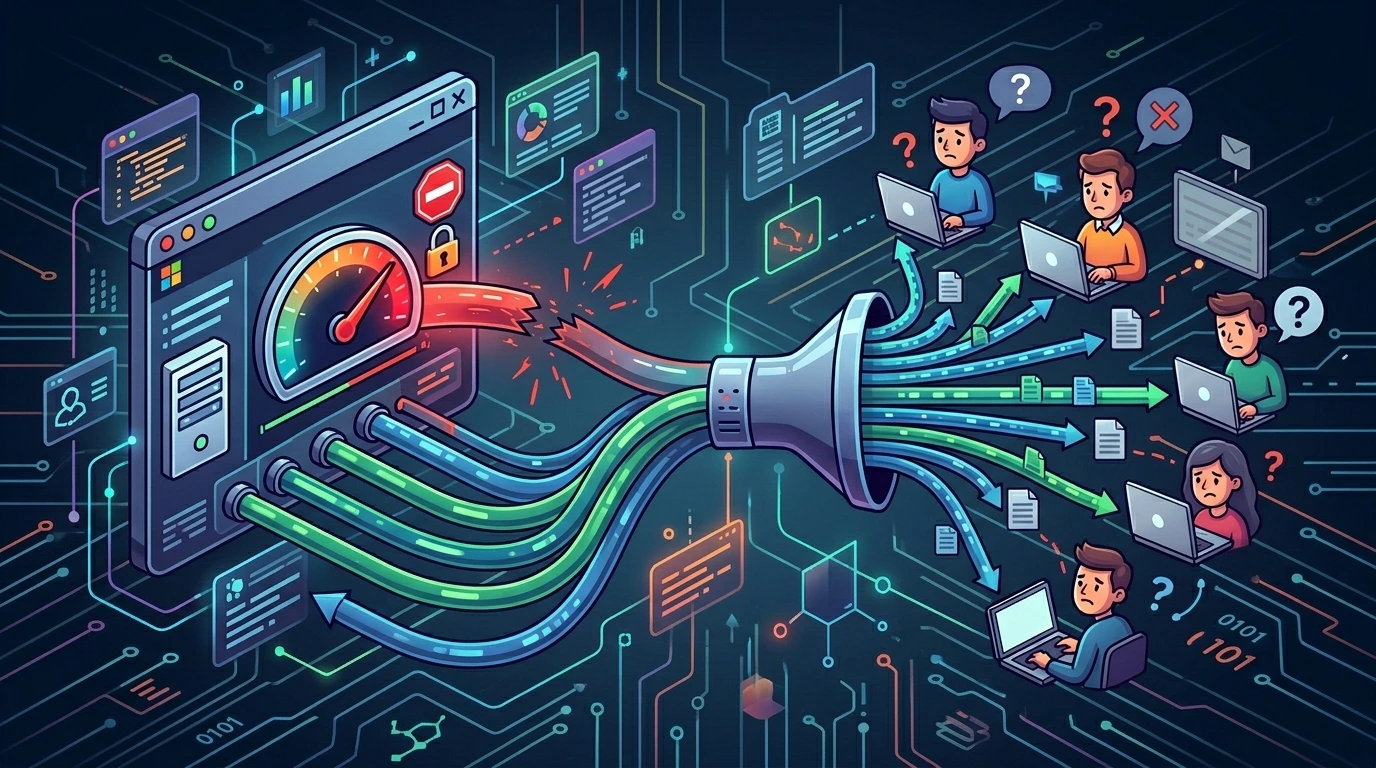
Mysterious Outlook Disconnections in a Corporate Network#
In this technical audit, I analyzed a complex email instability issue that frequently confuses network administrators. Multiple users in a corporate office reported that their Microsoft Outlook clients intermittently displayed status messages such as Disconnected, Trying to connect..., or requested credentials with the notice Need Password without an obvious pattern.
The first common suspicion falls on the local network, switches, link fluctuations, or individual Outlook profile corruptions. However, in networks with a high concentration of workstations behind a single outbound IP address, the root cause usually resides in the connection limits and throttling policies applied on the mail server (Exchange Server).
1. Network context and the symptom#
The environment under analysis had the following infrastructure characteristics:
- Local corporate network with dozens of workstations running Windows and having Outlook clients installed;
- A single outbound internet gateway sharing a single public IP via Network Address Translation (NAT);
- An Exchange server hosted locally (On-Premises) or remotely, receiving all email requests;
- Instability concentrated mainly during peak usage hours, such as the start of the business day at 08:00 or post-lunch breaks.
The classic symptom is a mass or block disconnection of users. While some machines work without issues, others on the same desk lose connectivity in a seemingly random fashion.
2. Why Outlook disconnects: the server is responsible#
Outlook acts as the client and attempts to maintain persistent connections open to synchronize folders, calendar information, and availability data. The operational bottleneck occurs on the Exchange Server. Under a NAT topology, all requests from internal workstations arrive at the server sharing the same source IP:
Workstation A (192.168.1.10) → NAT → Public IP: 203.0.113.50 → Exchange
Workstation B (192.168.1.11) → NAT → Public IP: 203.0.113.50 → Exchange
Workstation C (192.168.1.12) → NAT → Public IP: 203.0.113.50 → Exchange
...
Workstation N (192.168.1.N) → NAT → Public IP: 203.0.113.50 → Exchange
From the perspective of Exchange's receiving daemons, it is not dozens of independent users connecting, but rather a single remote host (203.0.113.50) opening hundreds of concurrent connections. Exchange interprets this flood of connections as a malicious pattern - such as a Denial of Service (DoS) attack or credentials harvesting - and starts rejecting subsequent connections.
3. Initial diagnosis and forensic log collection#
The first step in the diagnosis is to inspect the error logs on the Exchange server. The Windows Event Log under the Application scope will log MSExchange errors with specific event IDs:
Event ID: 4999
Source: MSExchange Common
Category: General
Type: Error
Description: Watson report about to be sent for process id: 12345,
with parameters: E12IIS, c-RTCComponent-CalendarProvider,
System.Web.HttpException, The connection limit for the IP address
203.0.113.50 has been exceeded.
In addition to the Event Viewer, Internet Information Services (IIS) logs - which host the Exchange HTTP endpoints (such as MAPI and EWS) - will display responses with the HTTP 429 status code:
2025-05-01 08:00:15 203.0.113.50 POST /mapi/emsmdb/ - 443 - 203.0.113.50 MSRPC/... 429 0 64 150
# HTTP 429 Too Many Requests -> Connection throttled by the server
This evidence proves that the disconnection is not due to physical link failures, but rather to a programmatic rejection by the web mail server.
4. Identifying the protocols in use#
The fix to be applied depends on the protocol configured on the Outlook clients. In the Exchange Management Shell (EMS), the status of the components and active limits are audited by running the cmdlets:
# Verify the operational state of Exchange components
Get-ServerComponentState -Identity EXCHANGE_SERVER | Select-Object Component, State

# Audit current IMAP4 configuration
Get-ImapSettings | Select-Object MaxConnectionsFromSingleIP, MaxConnections

# Audit current POP3 configuration
Get-PopSettings | Select-Object MaxConnectionsFromSingleIP, MaxConnections

# List global Exchange Throttling configurations
Get-ThrottlingPolicy | Select-Object Name, RCAMaxConcurrency, EWSMaxConcurrency, OWAMaxConcurrency
Identify which delivery channel is being consumed according to the table below:
| Protocol | Outlook Connection Type | Workload (Exchange) |
|---|---|---|
| MAPI/HTTP or MAPI/RPC | Corporate Exchange Profile | RCA (Remote Client Access) |
| EWS | Calendar, Out of Office (OOF) Services | EWS (Exchange Web Services) |
| IMAP | Manual IMAP Configuration | IMAP |
| POP3 | Manual POP Configuration | POP |
| ActiveSync | Outlook Mobile / Smartphones | EAS (Exchange ActiveSync) |
5. DNS verification and autodiscover resolution#
DNS integrity is fundamental to ensure that workstations correctly resolve mail server paths and locate the automatic discovery service (Autodiscover). If Autodiscover fails, Outlook will lose endpoint routes and attempt to reconnect constantly, exceeding connection limits.
Execute DNS records verification using PowerShell:
# Validate resolution of the main Exchange hostname
Resolve-DnsName mail.company.com -Type A

# Validate the MX record responsible for mail routing
Resolve-DnsName mail.company.com -Type MX

# Validate the internal and external Autodiscover SRV record
Resolve-DnsName _autodiscover._tcp.company.com -Type SRV
After verifying DNS responses, validate the health of the Autodiscover services on the Exchange server itself:
# Run health check for the Autodiscover service on Exchange
Test-ServiceHealth -Identity EXCHANGE_SERVER
6. Verification and health of other exchange services and IIS#
Often, connection drops occur in cascade because interdependent Exchange services (such as IIS or Active Directory access) are overloaded or stopped, causing the server to activate resource throttling.
Verify the status of all critical Microsoft Exchange daemons:
# List status of all services starting with MSExchange
Get-Service MSExchange* | Select-Object Name, Status, StartType
Next, verify the running state of the IIS Web Server (World Wide Web Publishing Service), which serves as the transport for MAPI and EWS:
# Check the execution status of IIS
Get-Service W3SVC
Finally, make sure the Exchange server can communicate and query the Active Directory global catalog without latency restrictions:
# Test connectivity with the local Domain Controller
nltest /dsgetdc:company.com
7. Verification of firewall rules and ports#
Verifying the Windows Server Firewall and local network ports helps ensure that no partial blocking rules or IP-based filters are interfering with persistent email sessions.
Audit the active rules in the Windows Firewall using PowerShell:
# List all active firewall rules on the host
Get-NetFirewallRule | Where-Object { $_.Enabled -eq 'True' } | Select-Object DisplayName, Direction, Action
Additionally, verify which TCP ports are in the LISTENING state on the Exchange server:
# List connections and listening ports using netstat
netstat -an | findstr "LISTENING"
Essential ports that should be open include 80, 443 (for MAPI/HTTP, EWS, OWA), 143, 993 (for IMAP), and 110, 995 (for POP3).
8. Verifying ssl/tls and server certificates#
If the SSL/TLS certificate associated with Exchange services is expired or incompatible with the security protocols of modern clients, the HTTPS channel will fail silently during the TLS handshake, forcing cyclic reconnections and accumulating sessions under the NAT public IP.
List and inspect local Exchange security certificates:
# View certificate thumbprint, subject, and expiration details
Get-ExchangeCertificate | Select-Object Thumbprint, Subject, NotAfter
To proactively search for certificates close to expiration (less than 30 days of validity remaining), run:
# Locate certificates expiring within the next 30 days
Get-ExchangeCertificate | Where-Object { $_.NotAfter -lt (Get-Date).AddDays(30) }
To validate connection integrity from outside the server, run a manual encrypted connection check on the TLS endpoint:
# Test TLS connection via OpenSSL
openssl s_client -connect mail.company.com:587 -starttls smtp
9. Verifying performance and system resources#
Exhaustion of CPU, RAM, or processing queue limits on Exchange can cause the server to apply severe throttling to preserve host stability.
Use PowerShell commands to extract host operational and resource status:
# Check general health of mailbox components on the Exchange server
Get-ServerHealth -Identity EXCHANGE -HealthSet "Exchange2016-Mailbox"

# Check physical RAM usage allocated to Exchange processes
Get-Process -Name "MSExchange*" | Select-Object Name, WorkingSet64

# Check transport queue metrics on the server
Get-ExchangeDiagnosticInfo -Server EXCH -Process EdgeTransport -Component QueueMetrics
10. Auditing and monitoring security logs#
A sudden flood of connections from the same corporate IP could indicate persistent brute force attempts or malicious login patterns on compromised accounts in the office, triggering automatic security policies.
Monitor failed login attempts in the system audit logs:
# List the latest 100 login audit failures
Get-EventLog -LogName Security -Newest 100 | Where-Object { $_.EntryType -eq "Failure Audit" }
Next, verify if there are any locked domain accounts in Active Directory:
# Locate accounts locked out for security reasons
Search-ADAccount -LockedOut | Select-Object Name, SamAccountName
To check generic security logs, run:
# List the latest 50 security events
Get-EventLog -LogName Security -Newest 50
11. Pre-configuration backup plan#
Before applying any changes to connection limits or creating new policies on the Exchange Server, it is mandatory to perform backups of the current configurations to ensure the ability to revert changes if necessary.
Parameter and configuration backup procedure#
Create a secure backup directory at C:/backup/ and export the current state of settings by running:
# 1. Export IMAP configurations
Get-ImapSettings | Export-Csv -Path "C:\backup\ImapSettings.csv"

# 2. Export POP3 configurations
Get-PopSettings | Export-Csv -Path "C:\backup\PopSettings.csv"

# 3. Export current throttling policies
Get-ThrottlingPolicy | Export-Csv -Path "C:\backup\ThrottlingPolicy-$(Get-Date -Format yyyyMMdd).csv"

# 4. Create a snapshot of the Exchange session state
Export-PSSession -Session (New-PSSession -ComputerName EXCHANGE) -OutputModule "C:\backup\ExchangeSession"
The backup files saved in C:/backup/ will serve as the baseline for recovery.
12. Adjusting maxconnectionsfromsingleip for IMAP and POP3#
If user profiles in the office connect via IMAP or POP3, Exchange limits concurrent connections per IP to very low values by default (typically 10 simultaneous connections).
# Check IMAP connection limit per IP
Get-ImapSettings | Select-Object MaxConnectionsFromSingleIP
# MaxConnectionsFromSingleIP : 10 (Restricted corporate default limit)
Limit calculation#
To estimate a safe connection limit for the NAT scenario, use the following formula:
Peak concurrent active users: 50
Concurrent folder connections per Outlook client (Inbox, Sent, Trash): ~3
Minimum connections needed from the NAT IP: 50 × 3 = 150
Recommended safe limit (+30% margin): 150 × 1.3 ≈ 200
Apply the new limits and restart the corresponding daemons:
# Apply new limit for IMAP connections per IP
Set-ImapSettings -MaxConnectionsFromSingleIP 200

# Apply new limit for POP3 connections per IP (if applicable)
Set-PopSettings -MaxConnectionsFromSingleIP 200

# Restart Exchange IMAP and POP3 services
Restart-Service MSExchangeIMAP4
Restart-Service MSExchangeIMAP4BE
Restart-Service MSExchangePOP3
Restart-Service MSExchangePOP3BE
13. Client throttling policies for MAPI, EWS and RCA#
For traditional corporate connections operating under MAPI over HTTP (RCA) or using Exchange Web Services (EWS), the server applies the Client Throttling Policies system. The default global policy limits concurrent sessions to low numbers per user.
Check the limits of the default global policy:
Get-ThrottlingPolicy -Identity "GlobalThrottlingPolicy_*" | Select-Object Name, RCAMaxConcurrency, EWSMaxConcurrency, OWAMaxConcurrency, EASMaxConcurrency
# RCAMaxConcurrency : 20
# EWSMaxConcurrency : 10
# OWAMaxConcurrency : 5
Create and apply a custom policy#
Create a new client throttling policy configured to tolerate NAT traffic concentration without overloading the Exchange server CPU:
# Create custom expanded policy
New-ThrottlingPolicy -Name "CorporateNATPolicy" `
  -RCAMaxConcurrency 100 `
  -EWSMaxConcurrency 50 `
  -OWAMaxConcurrency 20 `
  -EASMaxConcurrency 20
Associate the new policy with target mailboxes or service accounts:
# Associate the policy with a specific mailbox
Set-ThrottlingPolicyAssociation -Identity "user@company.com" -ThrottlingPolicy "CorporateNATPolicy"

# Associate in bulk for all users in an Organizational Unit (OU)
Get-Mailbox -OrganizationalUnit "OU=Finance,DC=company,DC=com" | Set-ThrottlingPolicyAssociation -ThrottlingPolicy "CorporateNATPolicy"
To audit which accounts already have custom policy associations active, run:
# Display users with custom policies
Get-ThrottlingPolicyAssociation | Where-Object { $_.ThrottlingPolicy -ne $null } | Select-Object Identity, ThrottlingPolicy
14. Post-configuration validation procedure#
After applying the IMAP/POP connection limits or associating new throttling policies, execute a structured validation playbook to verify Exchange connectivity stability.
Run the post-implementation check cmdlets in PowerShell:
# 1. Validate that the connection limit per IP has been updated
Get-ImapSettings | Select-Object MaxConnectionsFromSingleIP

# 2. Query recent Event Logs for recurring MSExchange throttling errors
Get-EventLog -LogName Application -Source "MSExchange*" -Newest 50 | Where-Object { $_.EntryType -eq "Error" }

# 3. Monitor active Exchange resource throttling diagnostics
Get-ExchangeDiagnosticInfo -Server EXCH -Process EdgeTransport -Component ResourceThrottling
Manual Test Step: Request that 3 to 5 users at different desks in the office launch their Outlook clients simultaneously. Check that the client status remains Connected to Microsoft Exchange and ensure that no new Event ID 4999 errors or HTTP 429 responses are logged.
15. Continuous monitoring strategy#
To prevent unexpected connectivity blocks as the company expands and NAT traffic volume increases, configure automated monitoring check scripts.
Create the validation PowerShell script at C:/backup/monitor-exchange.ps1:
# Check current throttling parameters script
$throttle = Get-ThrottlingPolicy | Where-Object { $_.Name -like "GlobalThrottlingPolicy*" }
if ($throttle.RCAMaxConcurrency -lt 20) {
    Write-Warning "WARNING: RCAMaxConcurrency is below recommended value: $($throttle.RCAMaxConcurrency)"
} else {
    Write-Output "Exchange Throttling Policies Status: OK"
}
Schedule this script to run periodically in the Windows Task Scheduler, or integrate it with monitoring systems (such as Zabbix, Grafana, or Prometheus).
16. Rollback and emergency reversion playbook#
If Exchange Server resource usage climbs unsafely after limits are expanded, immediately revert configuration parameters to original baseline values.
Run the rollback commands in the Exchange Management Shell (EMS):
# 1. Revert IMAP service limits
Set-ImapSettings -MaxConnectionsFromSingleIP 10

# 2. Revert POP3 service limits
Set-PopSettings -MaxConnectionsFromSingleIP 10

# 3. Remove custom throttling associations from mailboxes
Get-Mailbox -ResultSize Unlimited | Set-ThrottlingPolicyAssociation -ThrottlingPolicy $null

# 4. Remove the custom throttling policy from Active Directory
Remove-ThrottlingPolicy -Identity "CorporateNATPolicy" -Confirm:$false

# 5. Restart mail services to flush active sessions from memory
Restart-Service MSExchangeIMAP4, MSExchangeIMAP4BE, MSExchangePOP3, MSExchangePOP3BE
17. Exchange connectivity troubleshooting checklist#
Use this step-by-step checklist during triage of Outlook connectivity drops under NAT:
- [ ] General Diagnostics: Check Windows Application Event logs for
MSExchangeerrors. - [ ] IIS Audit: Inspect IIS access logs for HTTP
429or503responses. - [ ] NAT Mapping: Identify the corporate public NAT IP and check for concentrated connections.
- [ ] Configuration Backup: Export active IMAP, POP3, and throttling policy settings to CSV backups.
- [ ] IMAP/POP Modification: Adjust the
MaxConnectionsFromSingleIPsettings in EMS. - [ ] Throttling Policies: Create and assign custom client throttling policies to corporate users.
- [ ] DNS Audit: Verify DNS resolution for mail hostname and check Autodiscover SRV records.
- [ ] Services Inspection: Ensure health of
MSExchange*daemons, IIS (W3SVC), and AD access. - [ ] Certificates Audit: Check SSL certificate expiration dates and verify handshakes via OpenSSL.
- [ ] Post-Implementation Check: Verify connection stability and set up continuous monitoring routines.
18. Throttling and network risk matrix#
| Risk Event | Severity | Technical Impact | Recommended Mitigation |
|---|---|---|---|
| Concurrent Connection Block | High | Reaching IMAP/POP connection limits per IP disconnects Outlook clients across the office. | Increase the MaxConnectionsFromSingleIP setting based on peak user estimations. |
| Exchange Throttling Active | High | Default settings limit MAPI sessions per user, causing synchronization drops. | Implement a custom ThrottlingPolicy and associate it with target users. |
| SSL Certificate Expiration | Medium | Expired certificates cause HTTPS handshake failures and trigger Outlook connection alerts. | Set up monitoring tasks to alert if SSL certificates are within 30 days of expiration. |
| System Resource Overload | Medium | Over-expanded limits could degrade Exchange CPU and RAM performance. | Monitor server performance metrics using Get-ServerHealth. |
| DNS / Autodiscover Misalignment | Low | Incorrect DNS entries prevent clients from locating Exchange services. | Routinely verify external and internal A, MX, and SRV records. |
Was this article helpful?
Leave a quick reaction to help prioritize future technical guides:
See also

This post is licensed under CC BY-NC.
Comments
Join the discussion below.
0 comments