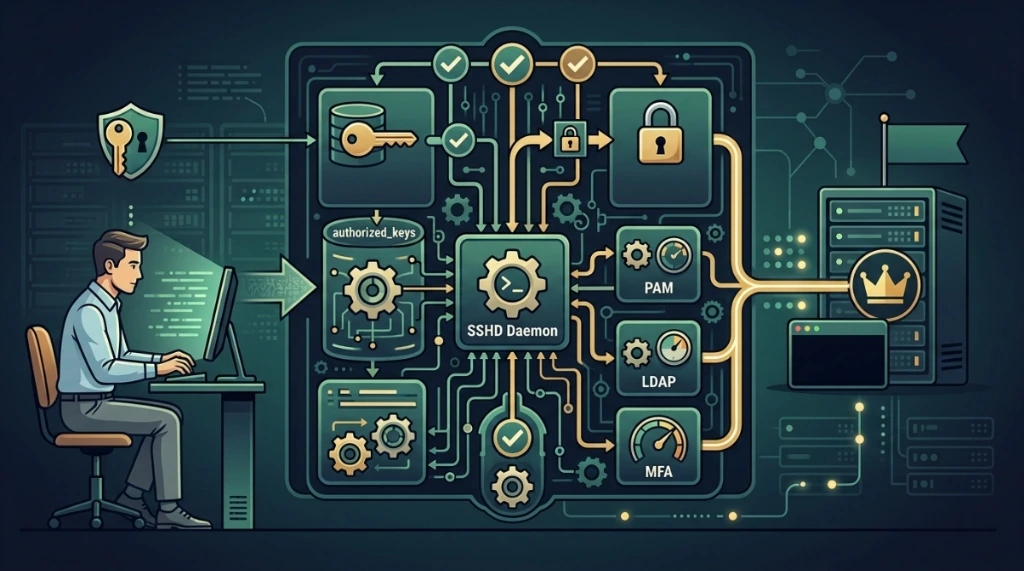
The guardian of UID 0#
Enabling root login via password is frequently discouraged in internet-exposed production environments. However, in out-of-band management architectures, isolated maintenance networks, or during infrastructure bootstrapping processes, understanding the execution flow is vital for low-level troubleshooting.
1. Surface configuration: sshd_config#
To allow root login with a password, the /etc/ssh/sshd_config file is modified. The critical parameters are:
# Explicitly allows UID 0 to authenticate
PermitRootLogin yes

# Enables the password authentication subsystem (keyboard-interactive interaction)
PasswordAuthentication yes
The "why" behind the commands:#
The default value for modern OpenSSH is prohibit-password. When set this way, the daemon allows root to log in only via public keys. If you attempt to send a password, sshd simply halts the password challenge flow for UID 0, even if the password provided is correct in /etc/shadow.
Expected Behavior: Upon executing systemctl reload sshd, the parent process (listener) receives a SIGHUP signal, rereads the configuration file, and updates its internal data structure (ServerOptions).
3. The PAM layer (pluggable authentication modules)#
Even with sshd_config set to yes, authentication can be denied by the operating system's PAM stack.
Critical File: /etc/pam.d/sshd
The role of pam_unix.so and pam_rootok.so#
sshd calls the pam_authenticate() function. If your system has the nullok flag disabled or if there are restrictions in the /etc/securetty file, PAM may block the login.
- Error Tracking: If you see
PAM: Authentication failurein the logs, the error is not insshd, but rather in the Linux authentication library attempting to validate the hash against/etc/shadow.
5. Edge cases#
Scenario a: blocking by "match block"#
At the end of sshd_config, there might be a Match block.
Match Address 192.168.1.0/24
PermitRootLogin no
How to Rule Out: Use sshd -T | grep -i permitrootlogin. This command prints the effective configuration the server is using after processing all Match blocks.
Scenario b: SELinux or AppArmor#
In distributions like RHEL or Debian with AppArmor, the context of the /etc/ssh/sshd_config file or the /usr/sbin/sshd binary might prevent certain actions.
- Verification Command:
ausearch -m avc -ts recentordmesg | grep -i "apparmor". - Rule Out: Temporarily put SELinux in permissive mode (
setenforce 0) to validate if the block persists.
Scenario c: "locked" root account#
If the password field in /etc/shadow starts with ! or *, PAM will reject the password regardless of what SSH says.
- How to Rule Out: Check with
passwd -S root. IfL(Locked) appears, executepasswd -u root.
Was this article helpful?
Leave a quick reaction to help prioritize future technical guides:
See also

This post is licensed under CC BY-NC.
Comments
Join the discussion below.
0 comments