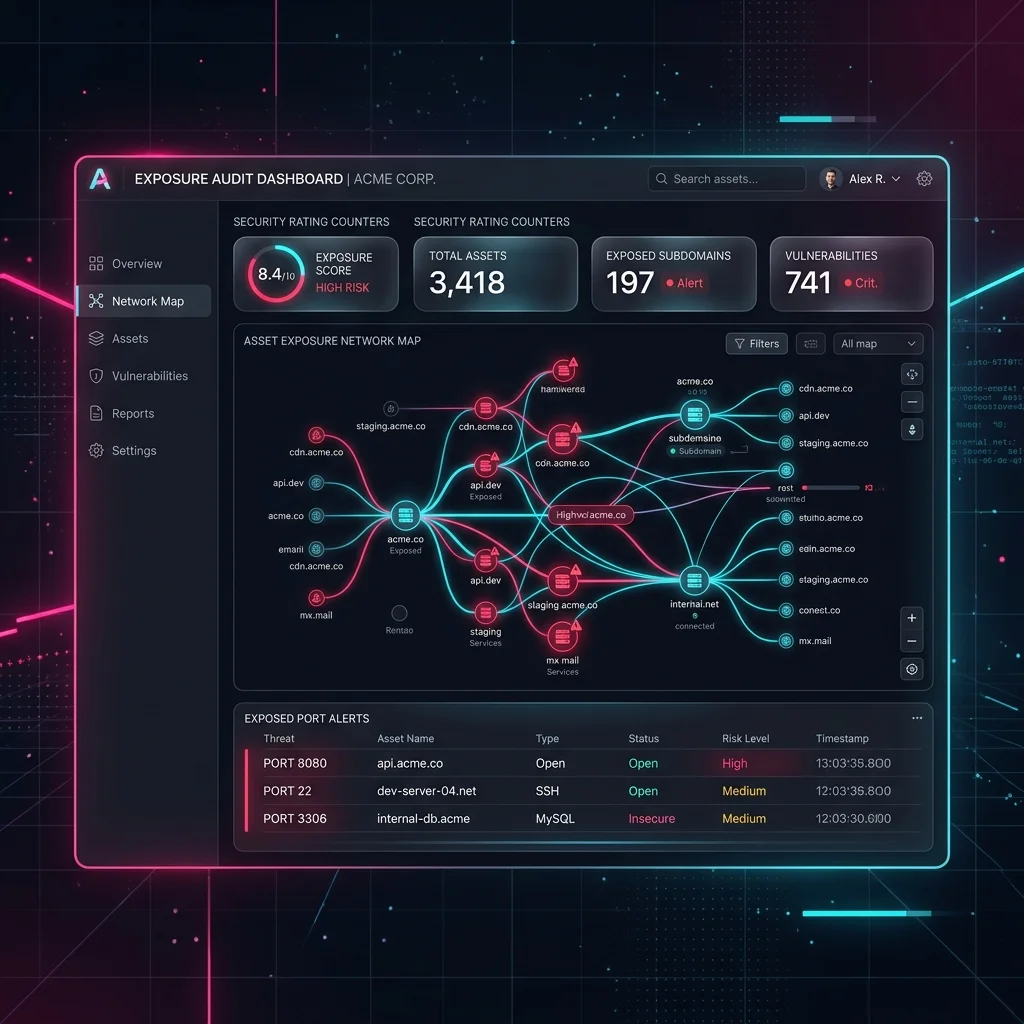
Approach Overview
Technical service focused on mapping and cataloging corporate assets directly accessible via the public internet (External Attack Surface), detecting accidental exposure of ports, subdomains, and logical vulnerabilities before threat actors exploit them.
Technical Lead: Percio Andrade Castelo Branco (Risk Analysis and Defensive Cybersecurity).
STAR Framework — Technical Dossier
1. Situation
Rapidly expanding corporate infrastructures frequently generate new subdomains, staging servers, cloud instances, and administrative panels that slip out of the control of central IT teams (shadow IT). Lacking visibility of the external attack surface, critical entry points such as database endpoints (MySQL/Postgres) and management consoles (SSH/RDP) end up exposed to the public internet with weak default credentials or outdated daemons, serving as entryways for ransomware campaigns or data exfiltration.
2. Task
Execute a comprehensive discovery and reconnaissance audit of all assets associated with the organization's public domains. This included mapping open network ports, fingerprinting service versions, identifying SSL/TLS configuration issues, and producing a prioritized remediation action plan based on the severity of the identified security risks.
3. Action
The audit process followed a controlled sequence of investigative mapping actions:
- Passive Reconnaissance (OSINT): Monitored public intelligence feeds and historical DNS logs to enumerate active and abandoned subdomains. Audited TXT, SPF, DKIM, and DMARC parameters to evaluate the organization's email domain security status.
- Non-Intrusive Active Scanning: Performed targeted, rate-limited port scans (common TCP and UDP ports) utilizing industry-standard tools like Nmap, optimized to avoid host service disruption or triggers.
- Banner Grabbing & Fingerprinting: Collected and parsed responses from open ports to determine exact operating system details and service daemon versions (e.g. Apache, Nginx, Dovecot, OpenSSH), cross-referencing results with known vulnerability databases (CVEs).
- Secure Communication Audits: Evaluated HTTP security headers on public-facing web applications and assessed SSL/TLS cipher suites for weak or deprecated algorithms.
- Threat Modeling & Risk Matrix: Classified all discovered vulnerabilities using the CVSS v3 framework, aligning them with the OWASP Top 10 to establish critical remediation priorities.
4. Result
The exposure audit delivered immediate visibility and actionable security improvements:
- Orphan Asset Discovery: Identified 18 old, unmapped subdomains linked to the primary domain. Three of these were hosting outdated staging setups with known PHP execution vulnerabilities.
- Exposed Port Mitigation: Detected and immediately restricted access to two database endpoints (MySQL and Redis) that were exposed to the public internet without strong authentication on auxiliary cloud instances.
- Compliance Roadmap: Delivered a prioritized technical roadmap and executive summary. The internal infrastructure team mitigated 100% of critical and high-severity risks in under 48 hours from delivery.
Technical Discovery Routines (Operational Sample)
Example commands used during the external attack surface audit:
# 1) Silently scan and identify service versions on a target host
nmap -sV -sC -O -F -T3 target-domain.com # 2) Deep scan on specific infrastructure and administration ports
# - Ports: SSH (22), MySQL (3306), Postgres (5432), RDP (3389), Redis (6379), Docker API (2375)
nmap -p 22,3306,5432,3389,6379,2375 -sV --script banner,vulners target-domain.com # 3) Audit SSL/TLS configurations and cipher suites supported on port 443
nmap -p 443 --script ssl-enum-ciphers target-domain.com
Discuss This Service
Looking to discover, catalog, and audit your organization's external attack surface to eliminate vulnerability exposures?