 PUBLISHED
Technical summary
NEXUS Threat Intelligence & AI Threat Hunting plugin integrating the four open APIs of the abuse.ch initiative and the NEXUS AI Engine: malware IOC lookups on ThreatFox, sample search by hash on MalwareBazaar, YARA/ClamAV rules on YARAify (with file upload) and malicious URLs on URLhaus — with 7-day local caching, real-time API status, AI forensic triage, MITRE ATT&CK mapping, SIEM hunting queries, YARA v4 rule authoring, and automatic signals in the Intelligence Hub.
Executed scope
- Modular Anti-Monolith Architecture:
plugin.php(actions and enricher registration),backend.php(HTTP, cache, install, history), andincludes/ai.php(forensic AI engine and YARA generator). - 4 abuse.ch Providers Integration:
- NEXUS Artificial Intelligence Engine (
includes/ai.php): - Database & Caching:
- Intelligence Hub Enrichment:
- Reactive Alpine.js UI (
tab.php): - Fastr Slash Commands:
- Internationalization (i18n): Full support for Portuguese (
pt_BR), English (en_US), and Spanish (es_ES).
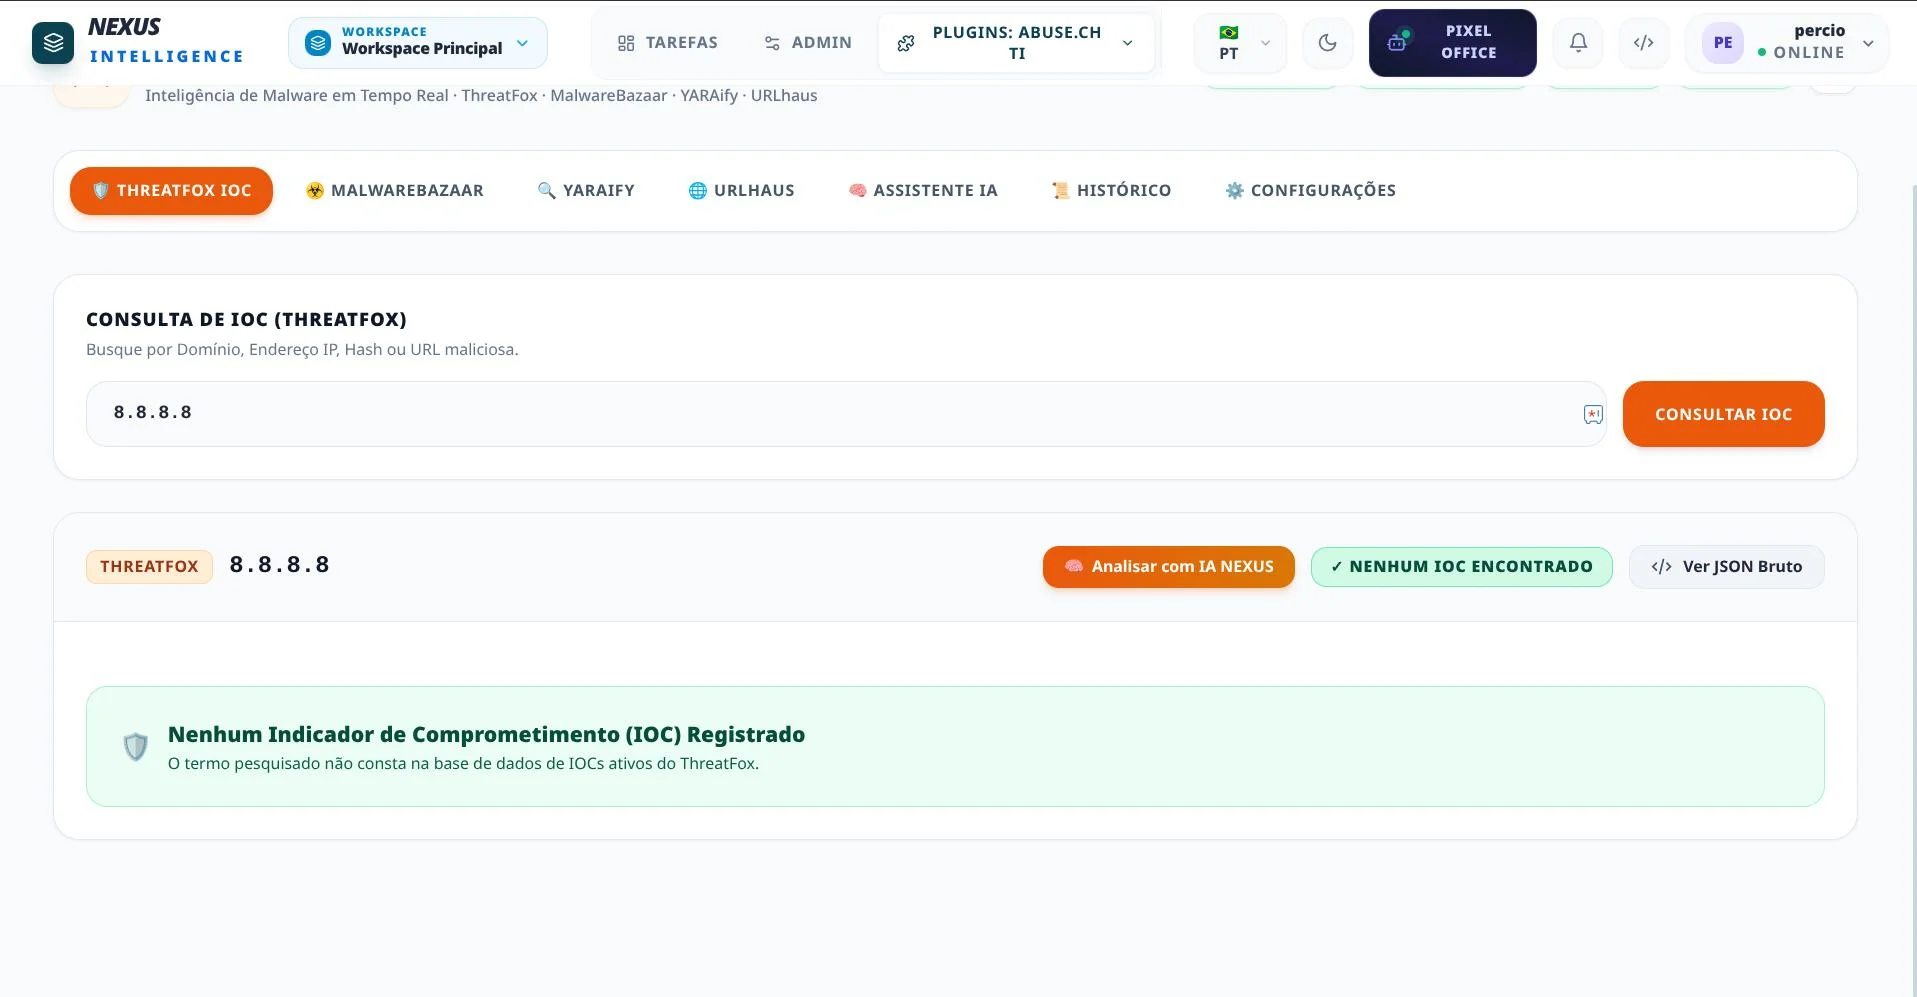
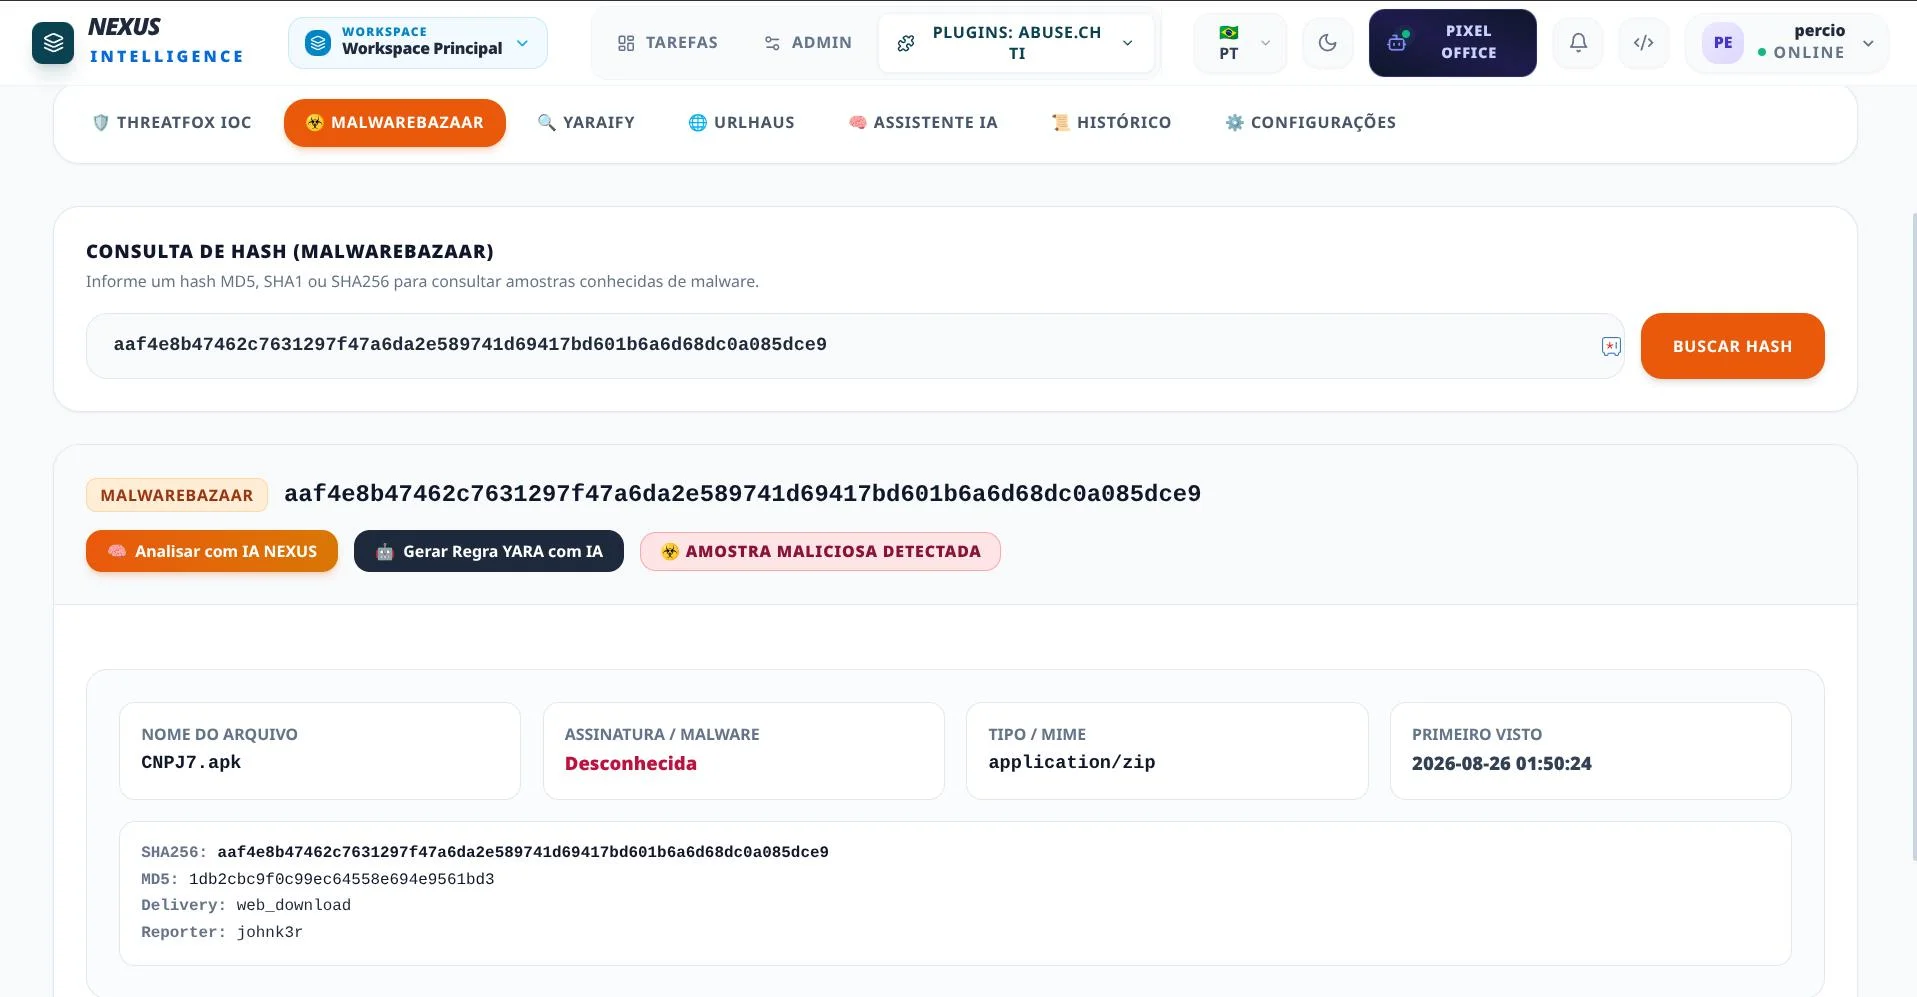
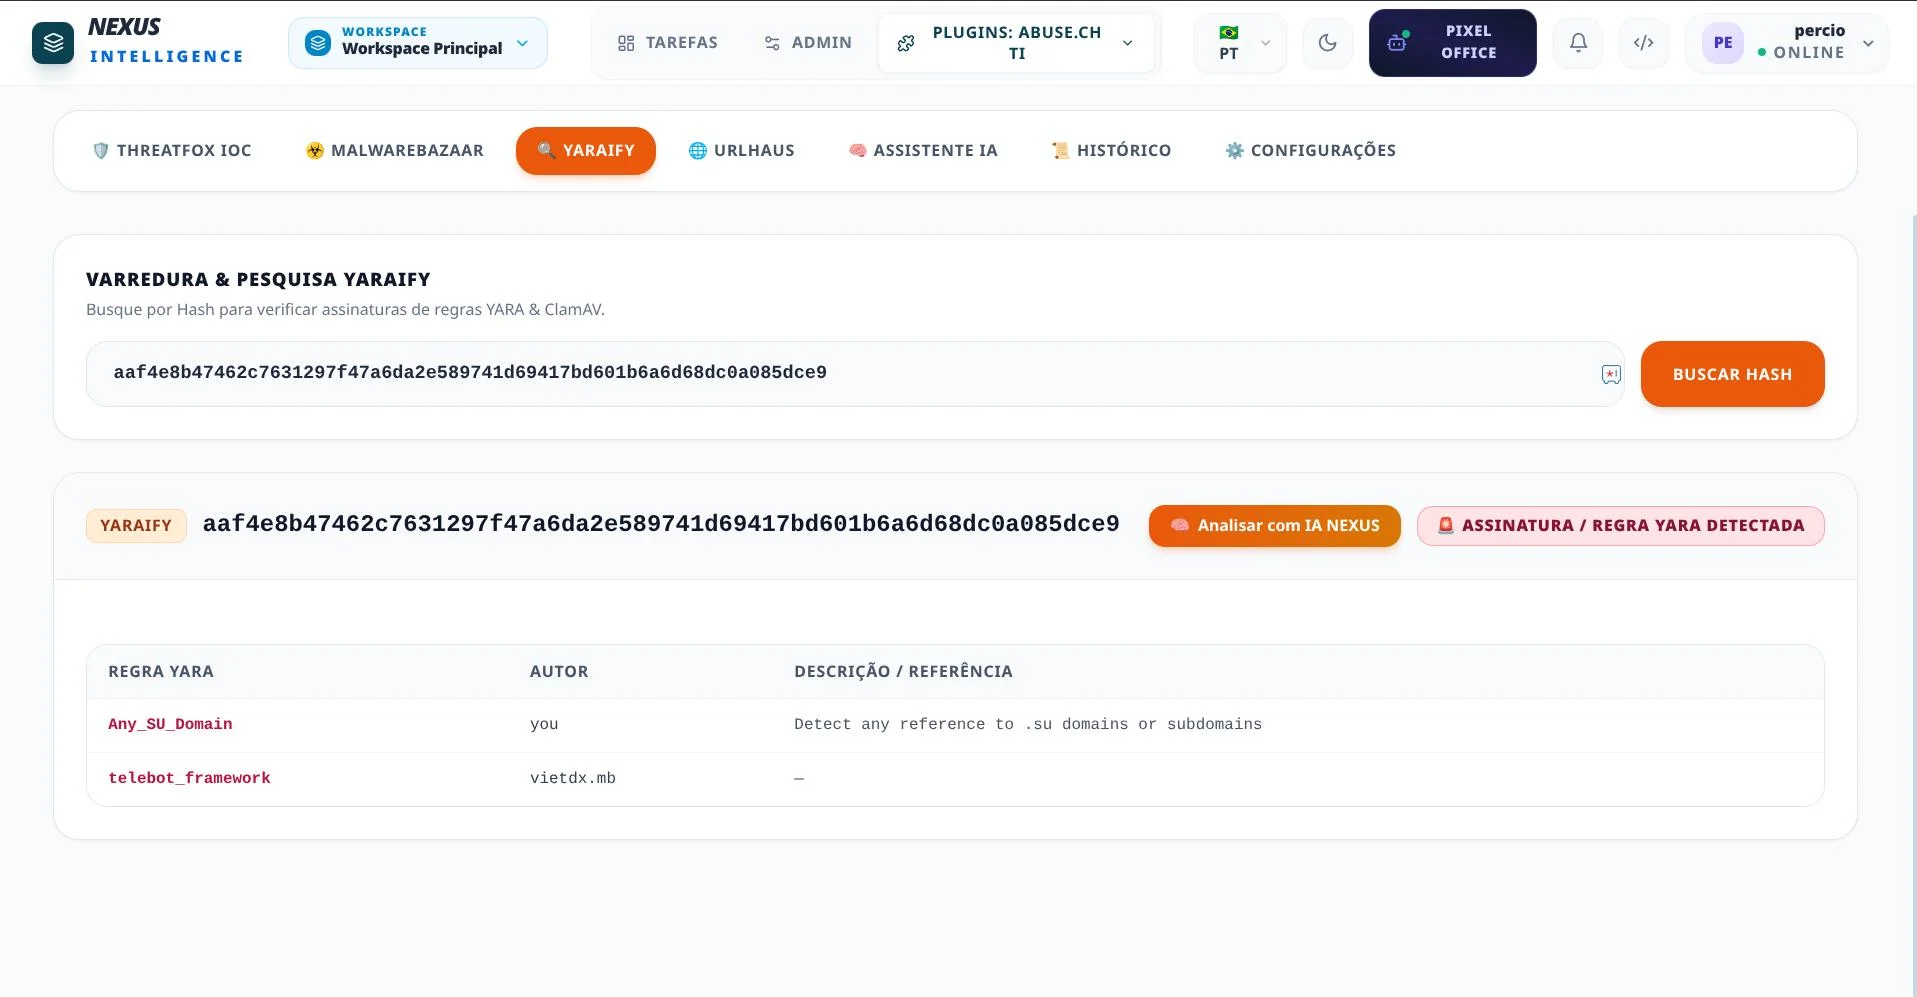
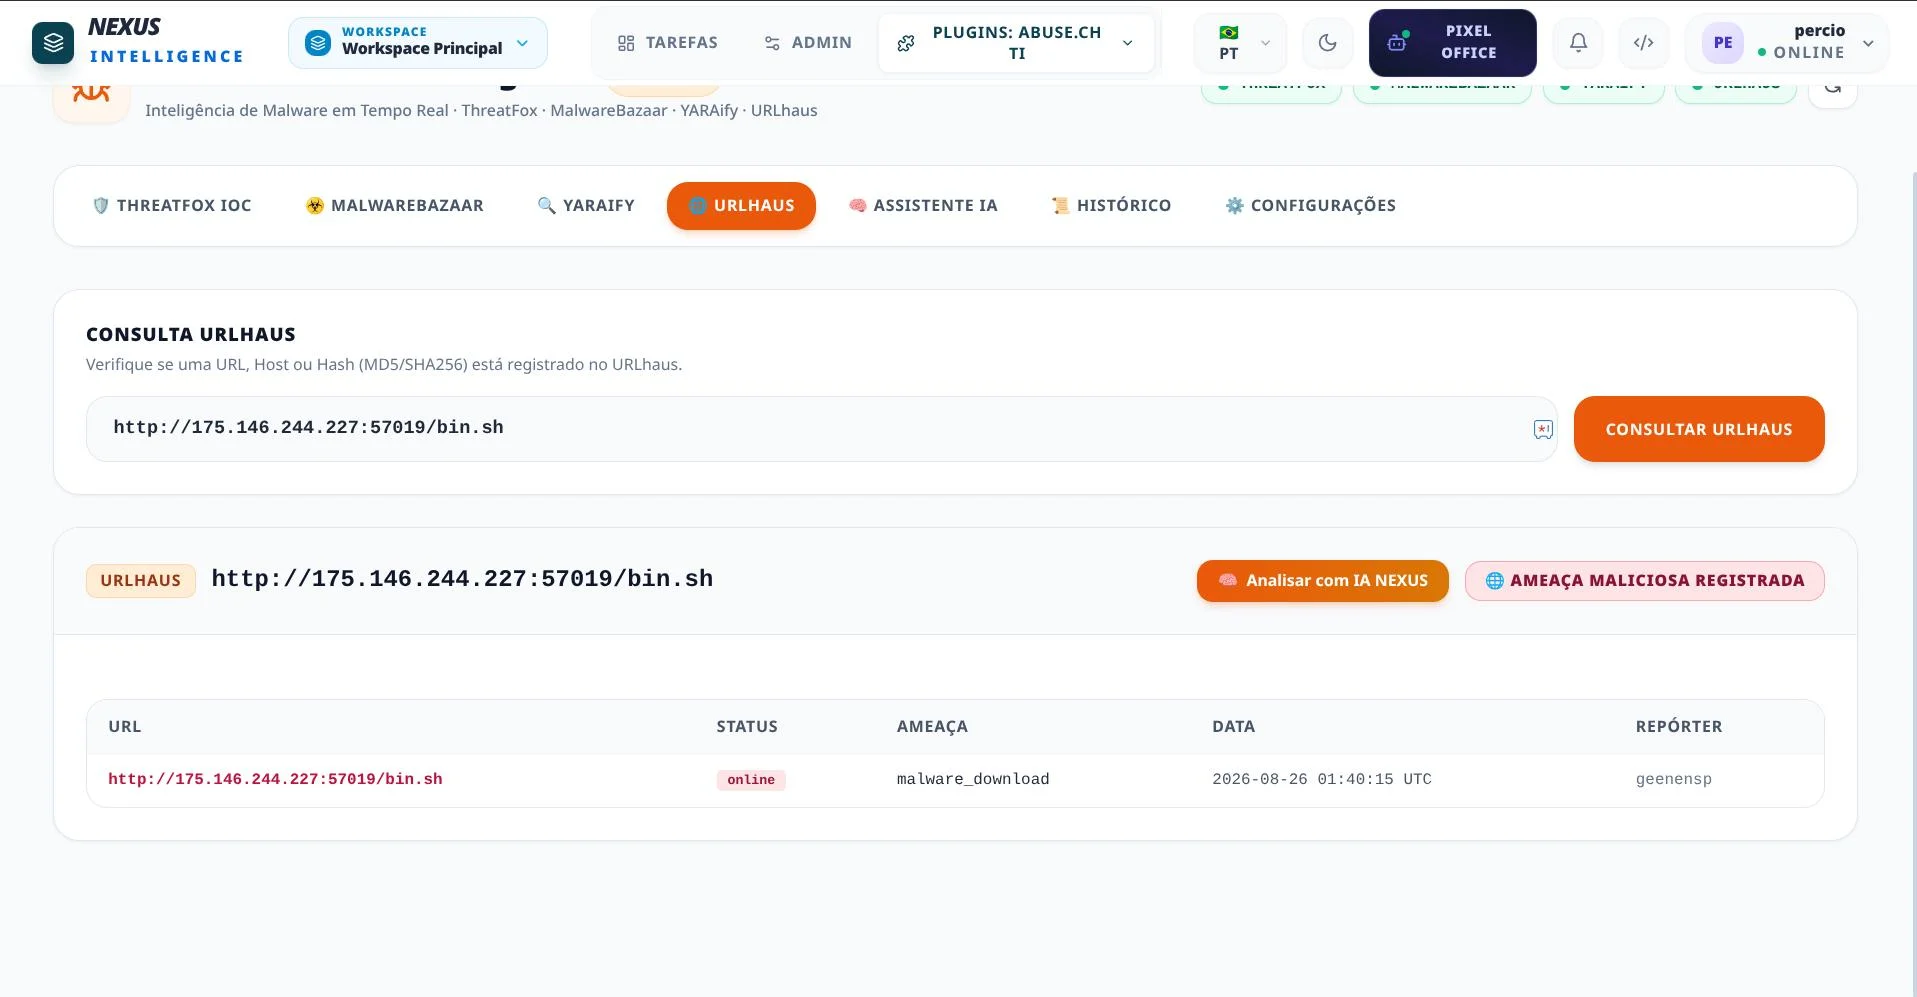
- ThreatFox: IOC lookup (IPs, domains, hashes, URLs) with C2 identification, malware families, confidence scoring, and first-seen timestamps. - MalwareBazaar: Sample lookup by MD5/SHA1/SHA256 hash, executable metadata, MIME types, delivery methods, and reporters. - YARAify: Signature search across community YARA rules and ClamAV engine, plus multipart upload support for binary scanning. - URLhaus: Verification of active malicious URLs and payload distribution hosts.
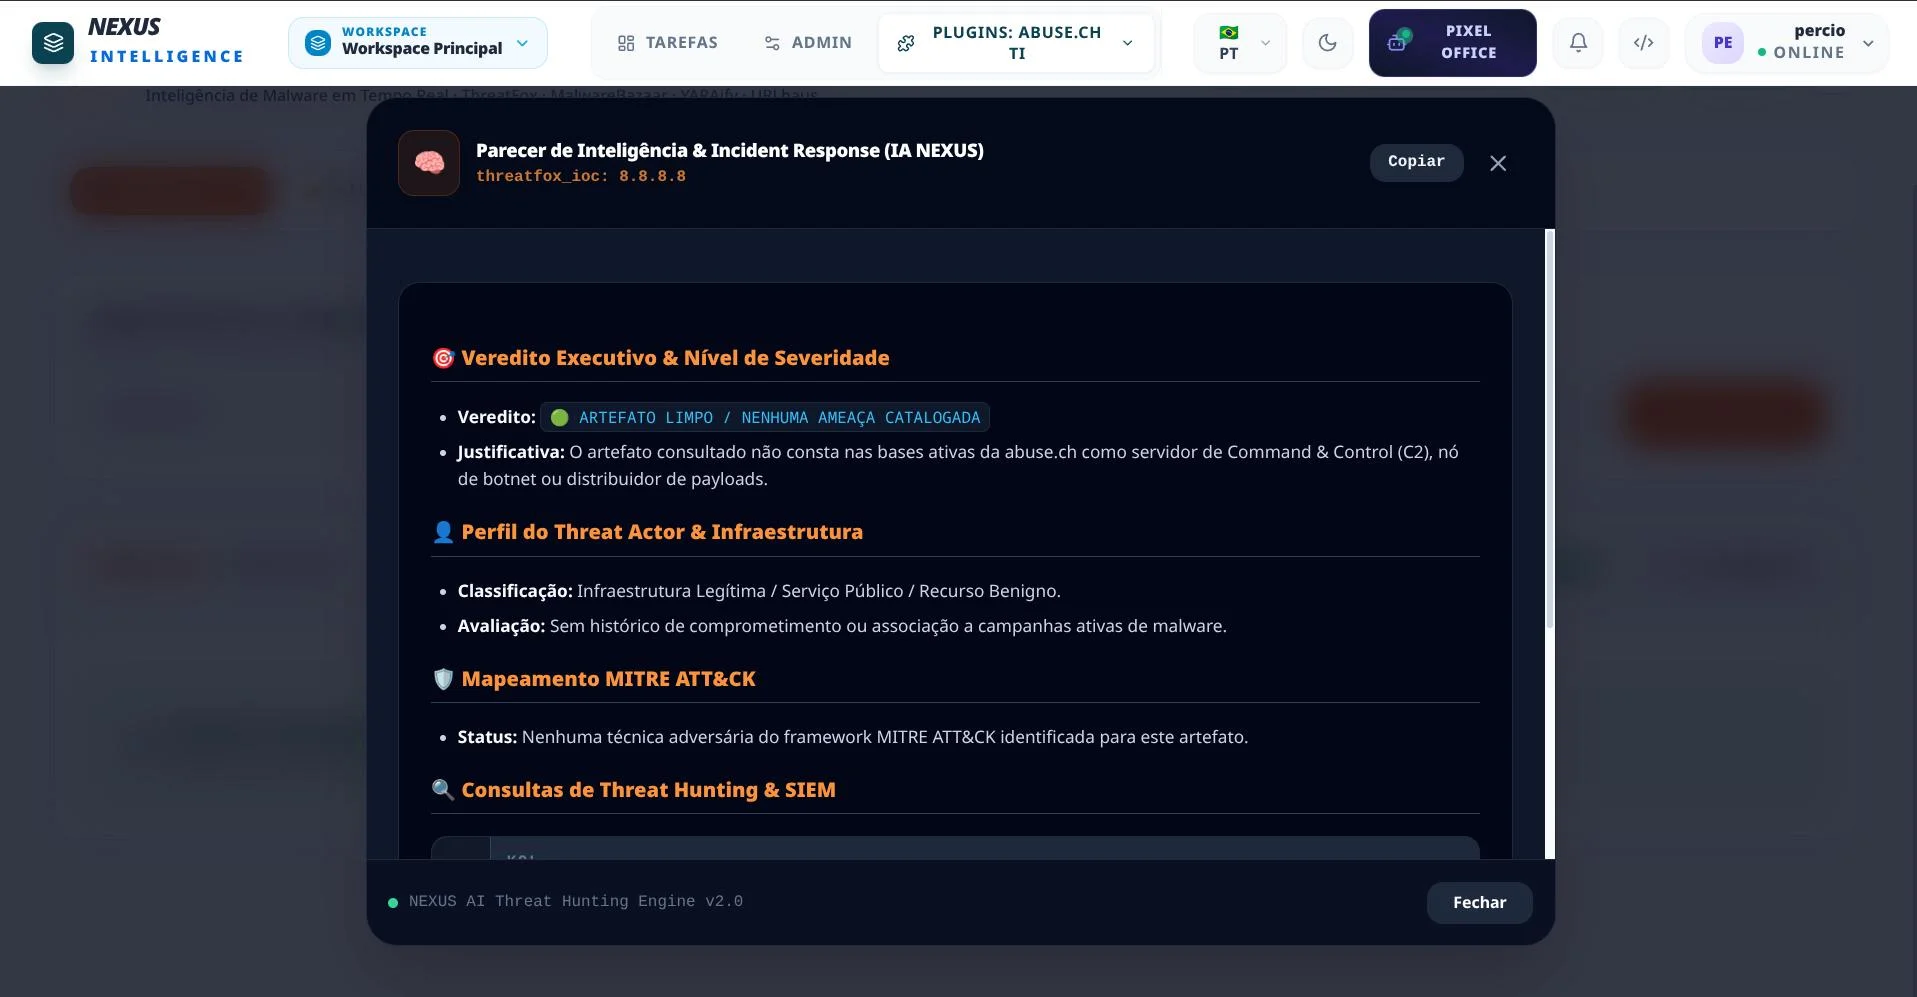
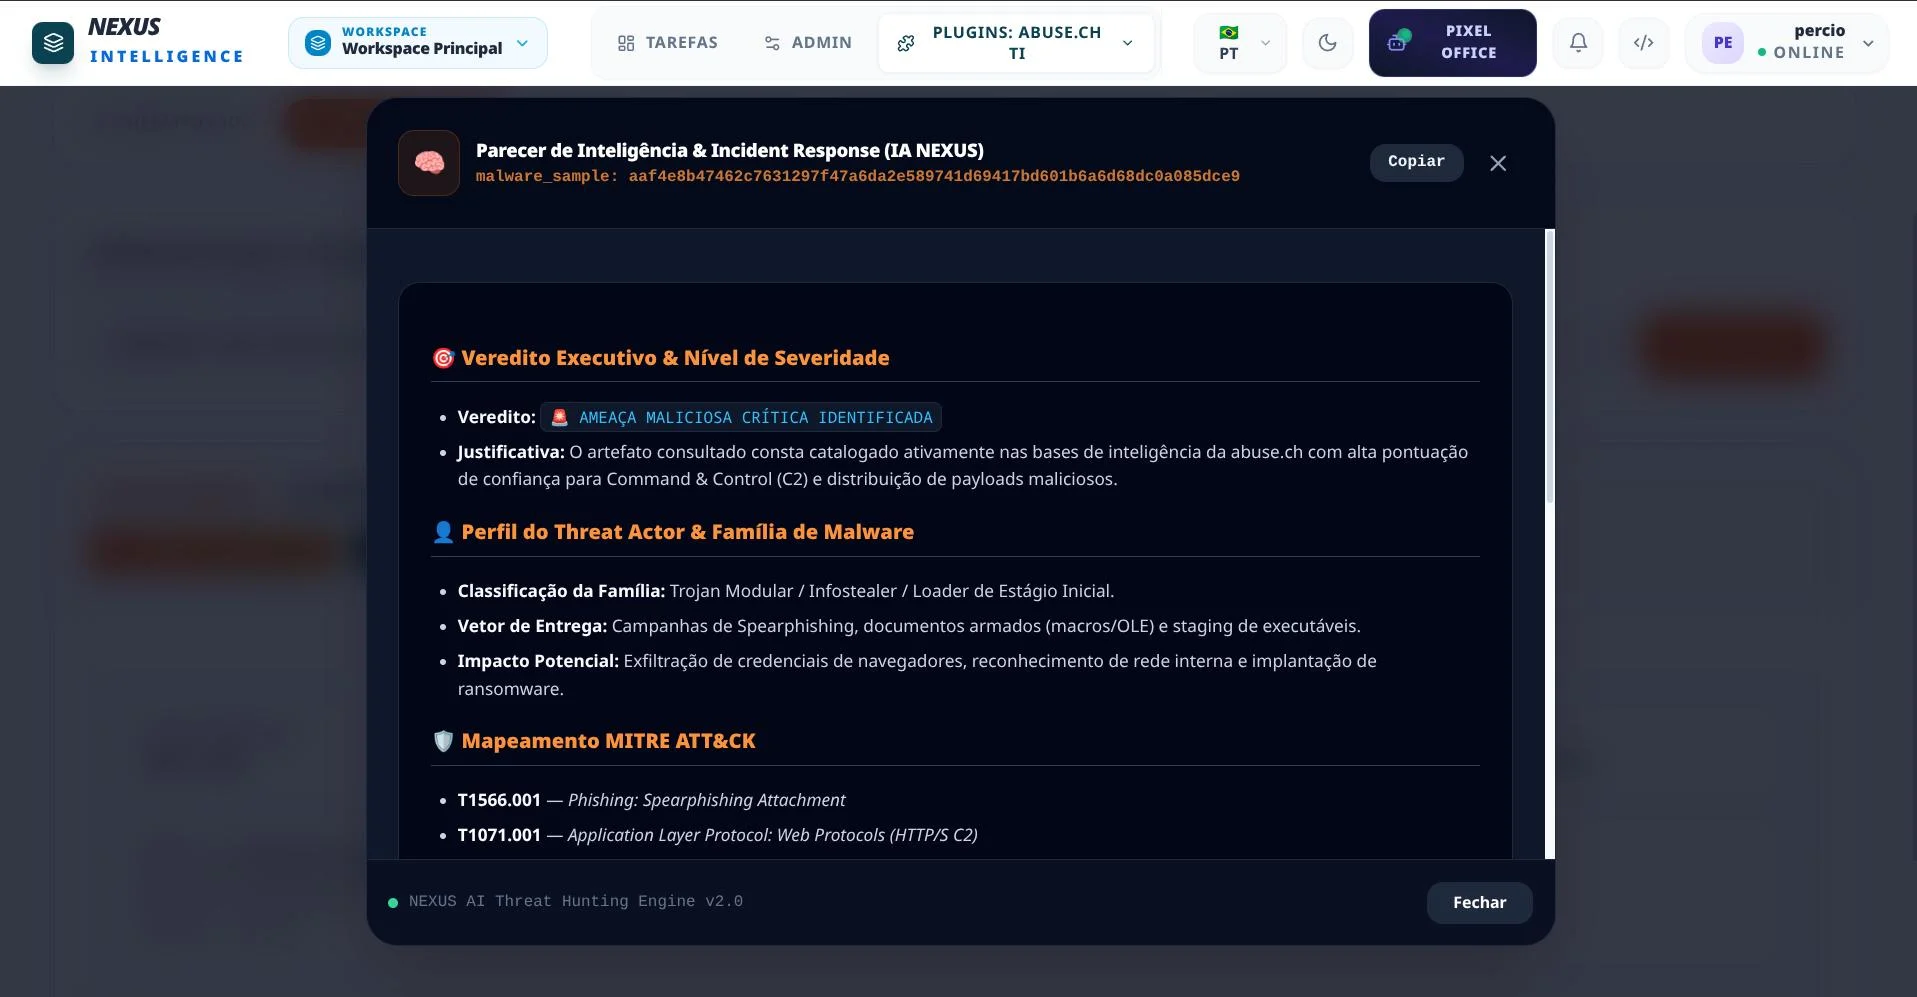
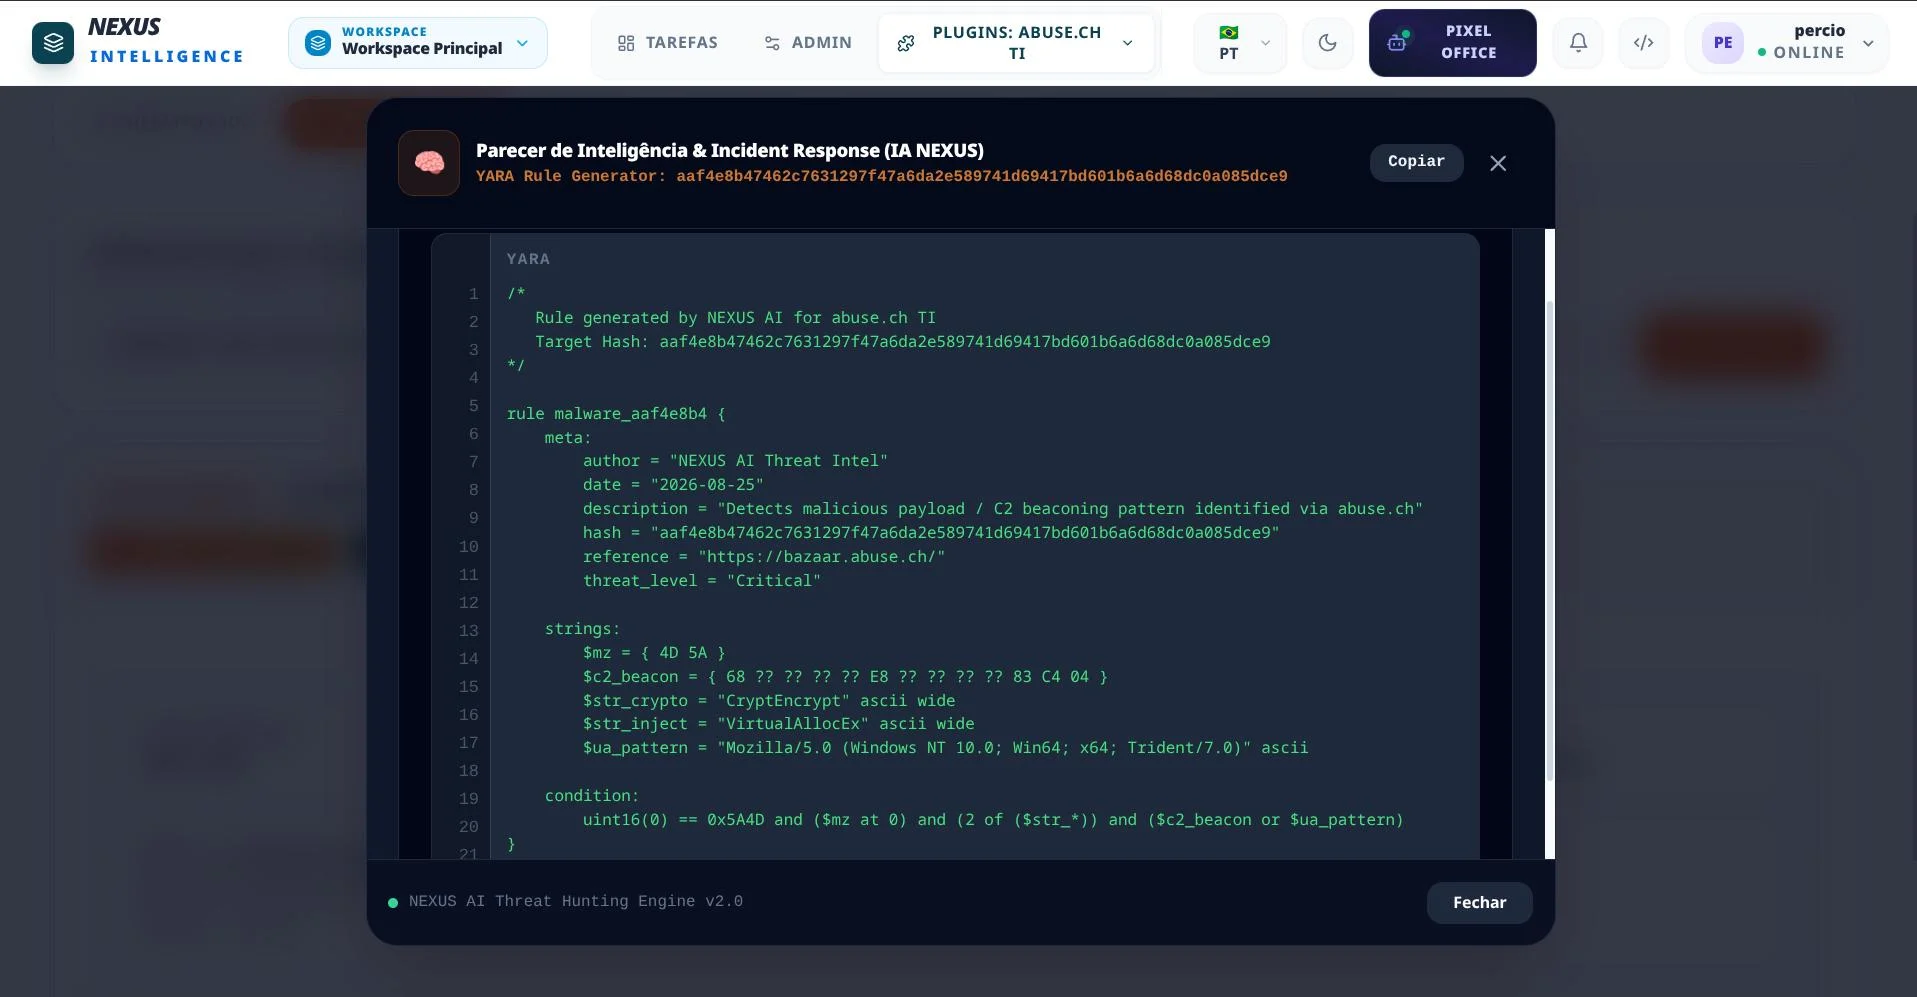
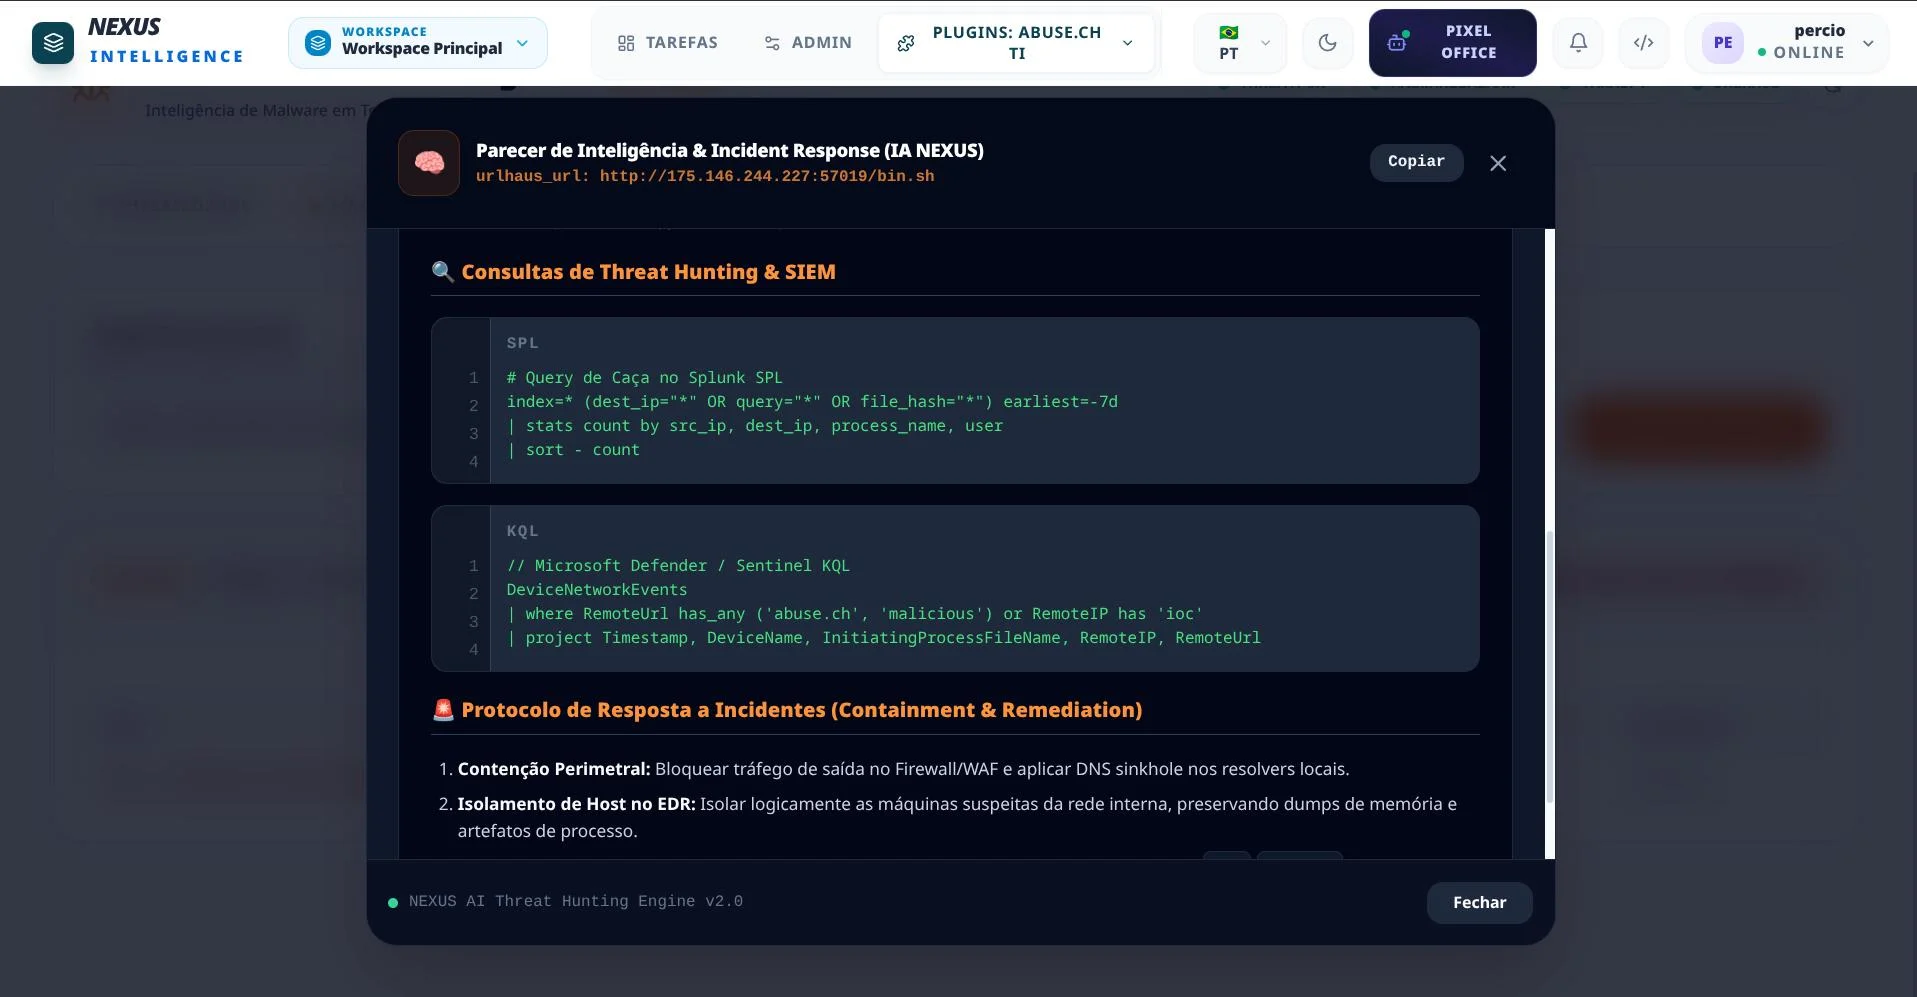
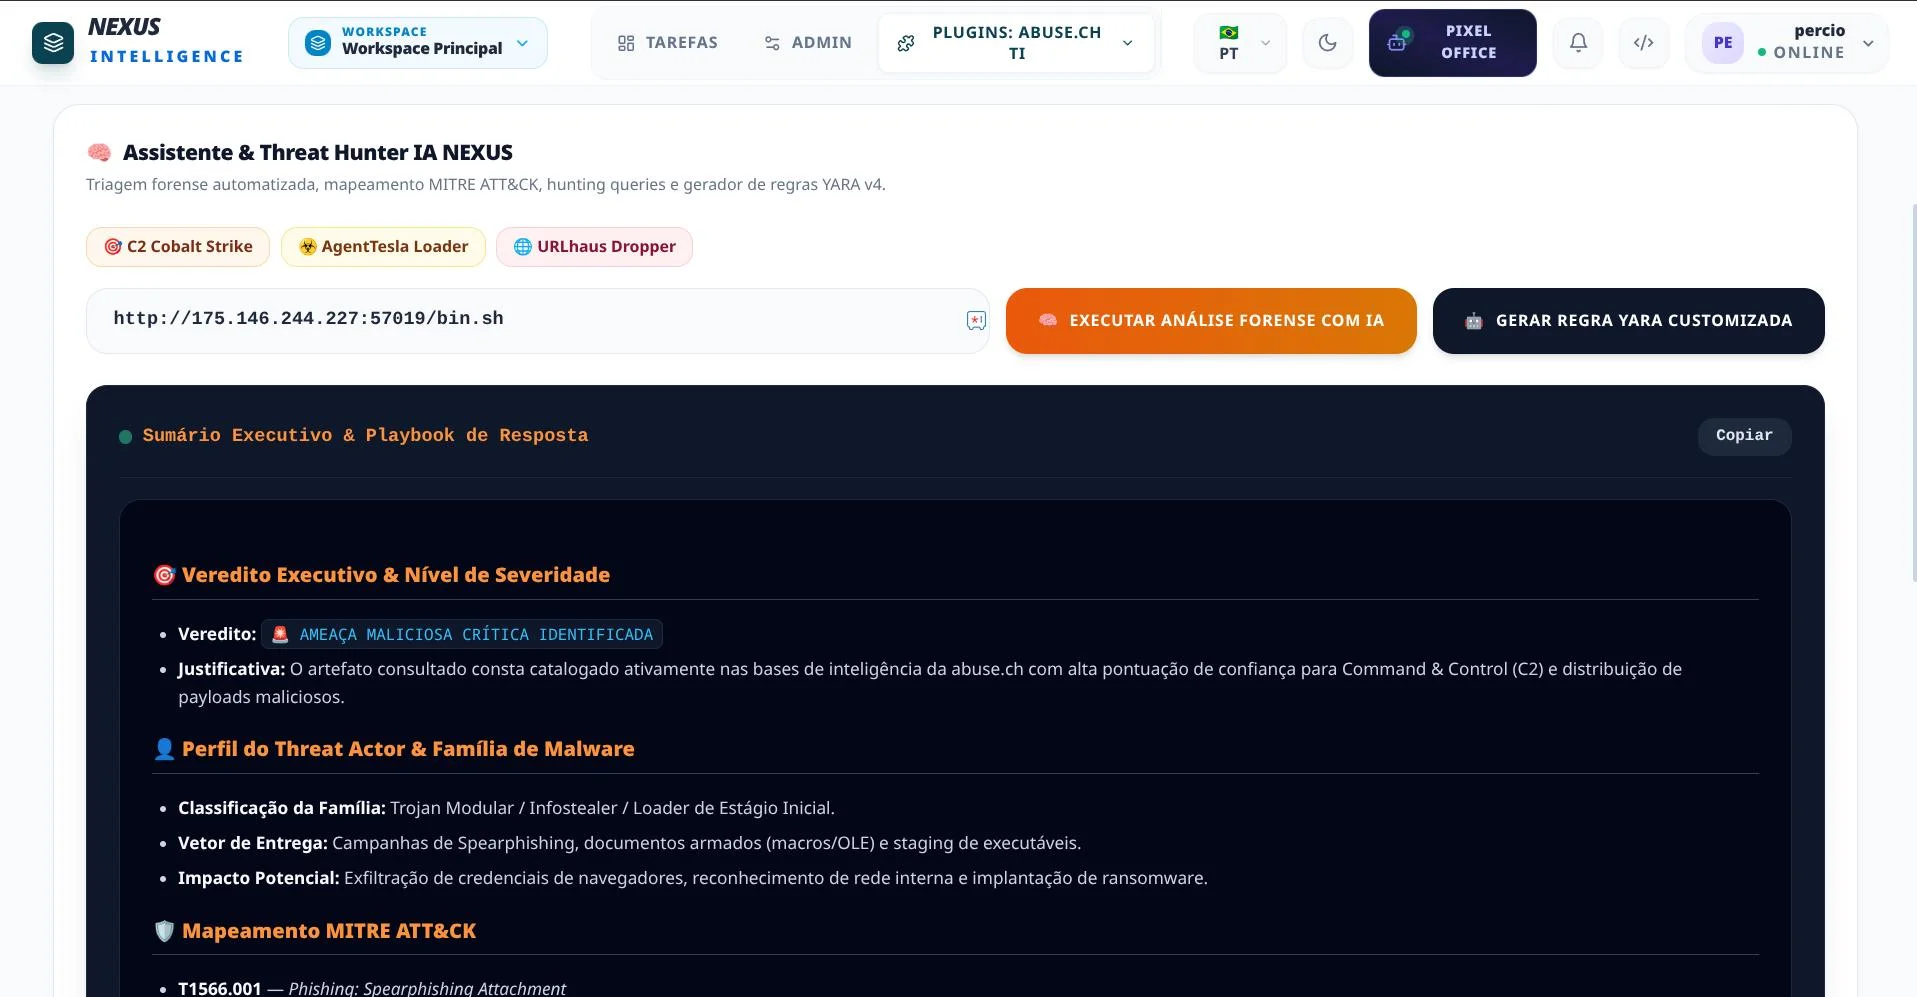
- 1-Click Forensic Triage: Generates executive verdicts with severity levels (including clean artifact recognition such as 8.8.8.8). - MITRE ATT&CK Mapping: Automatic alignment with adversarial techniques (T1566, T1071, T1059, T1027). - SIEM Threat Hunting Queries: Ready-to-use search syntax for Splunk SPL, Elastic KQL, Suricata, and Microsoft Defender KQL. - Incident Response (IR) Playbook: Perimeter containment, EDR host isolation, and persistence remediation steps. - YARA v4 Rule Generator: Automated creation of high-fidelity detection rules from sample hashes and behavioral metadata.
- abusech_cache table (7-day TTL with force bypass parameter). - abusech_history table for complete audit trails.
- Priority enricher (priority 60) monitoring artifacts (hash, domain, ip, url) across tasks and comments, emitting critical (MalwareBazaar) and high (ThreatFox) severity signals.
- Rich Markdown formatting with marked.js. - High-priority modal (z-[99999]) ensuring overlays stay on top of the NEXUS header. - Dedicated subtabs for ThreatFox, MalwareBazaar, YARAify, URLhaus, AI Advisor, History, and Settings.
- /threatfox <IOC>, /bazaar <HASH>, /yaraify <HASH>, /urlhaus <URL>, and /abusech-ai <IOC>.
Stack and tooling
- PHP 8.3 (Plain PHP / Modular Architecture)
- MySQL 8 (PDO Singleton,
abusech_cacheandabusech_historytables) - Alpine.js v3 + Tailwind CSS + Marked.js
- NEXUS AI Engine (
run_local_opencode/ AI Hub / Heuristic Engine) - cURL Client with secure timeouts and unified Auth-Key support
Operational tags
- Threat Intelligence
- Malware
- OSINT
- IOC
- YARA
- abuse.ch
- AI
- Plugin NEXUS
Operational outcome
- Instant malware triage and perimeter containment decisions directly within NEXUS.
- Real-time YARA v4 rule and SIEM query synthesis to counter active cyber attack campaigns.
- Automated task and comment enrichment without exhausting public API rate limits.
GitHub progress (issues)
Real-time panel with latest repository issues.
live feed
open issues on GitHubcarregando andamento...
não foi possivel carregar as issues agora. abra no github pelo link acima.
Real results
Advanced AI-powered Threat Intelligence & Threat Hunting hub integrating the four open APIs of the abuse.ch initiative (ThreatFox, MalwareBazaar, YARAify, and URLhaus) with the NEXUS AI engine for automated forensic triage, MITRE ATT&CK mapping, SIEM hunting queries, YARA v4 rule authoring, and 7-day local caching.
Architecture and organization
- PHP 8
- MySQL 8
- Alpine.js
- Tailwind CSS
- NEXUS AI
- Plugin NEXUS
Execution and operations
The project follows reproducible execution flow with technical validation in production-like environments.
Screenshots
Talk about this project
Apply this implementation pattern in your environment and accelerate delivery with technical consistency.